RBI opens Bhubaneswar Data Centre for RTGS, NEFT and cybersecurity institute
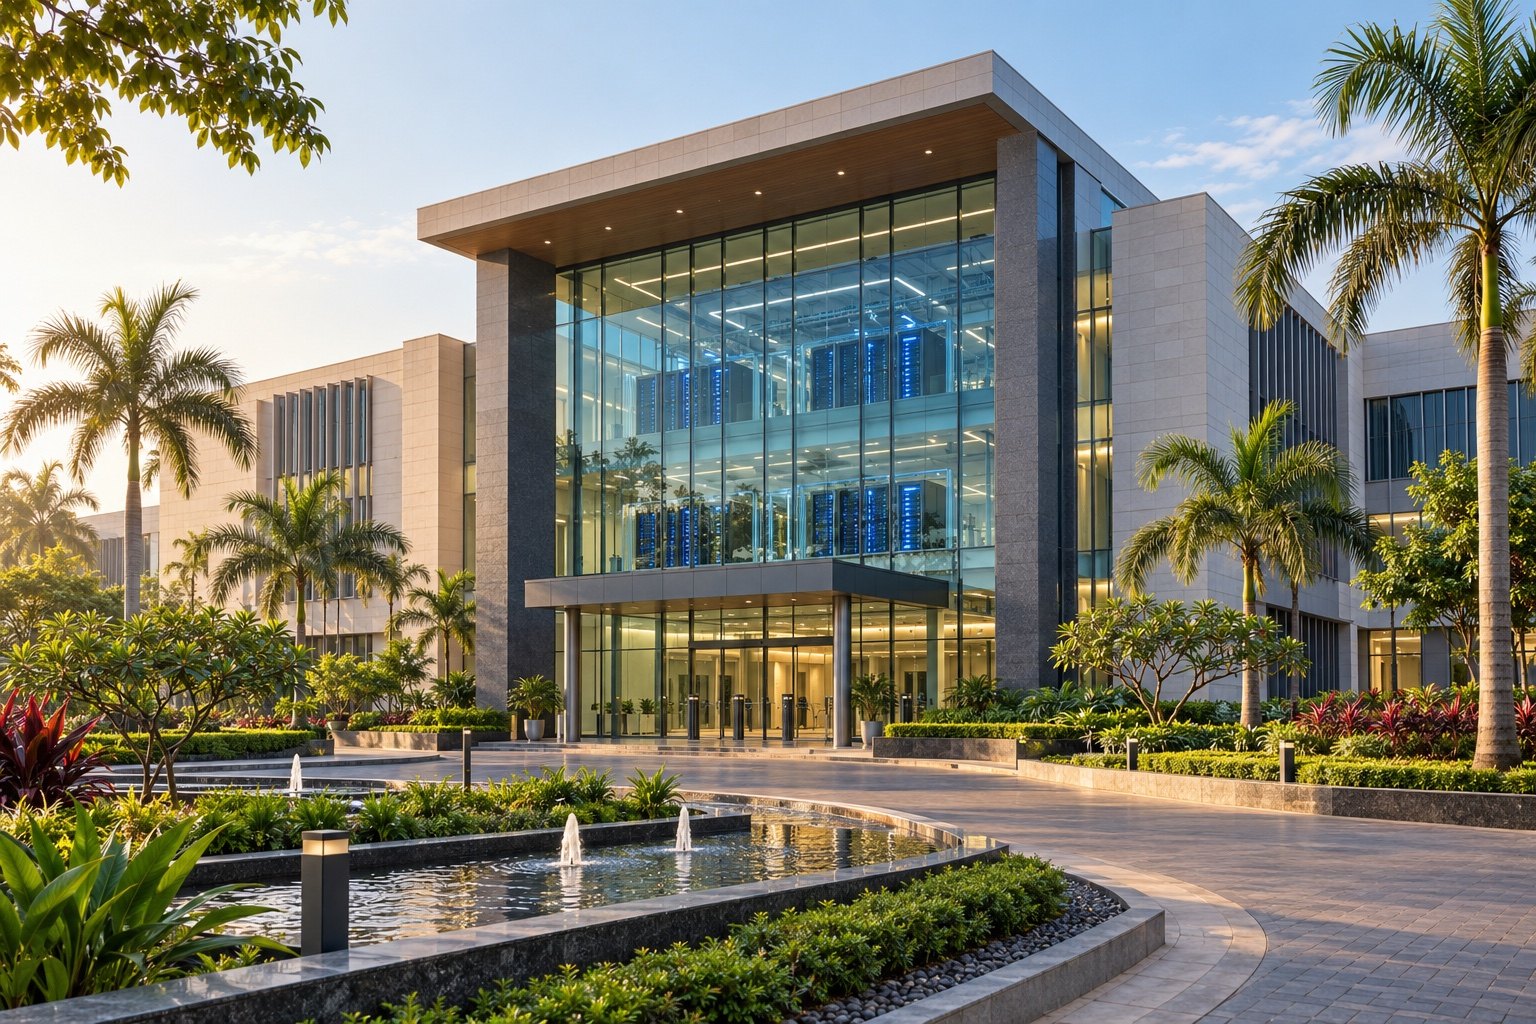
Prime Minister Narendra Modi inaugurated the Reserve Bank of India's Data Centre and Cybersecurity Training Institute in Bhubaneswar, Odisha, on 25 October 2026. The Data Centre will house the RBI's mission-critical systems, among them RTGS and NEFT, Finance Minister Nirmala Sitharaman said. She added that the Institute would build expertise in cybersecurity, artificial intelligence and other emerging technologies.
Syllabus: GS3 · Indian Economy & Growth; GS2 · Statutory & Regulatory Bodies; GS3 · Cyber Security & Money Laundering
Why this matters for UPSC
GS3 covers the basics of cyber security. Prelims can ask what CERT-In, CSIRT-Fin and NCIIPC do under the Information Technology Act, 2000, and how RTGS and NEFT settle payments; GS3 Mains, how to make the financial sector cyber-resilient.
Why it matters
A salary credit, a rent transfer or a company's large payment to a supplier can move through NEFT or RTGS, and the RBI runs both. If those systems stop or are breached, money stops moving between banks across the country, not just at one bank. A data centre built to keep running when equipment fails, as the PMO says this one is, cuts the risk that a single fault halts payments. Lenders also need staff who can spot and contain an attack quickly, and the new institute is meant to train them. The larger issue is that digital banking has widened what attackers can hit: a breach can drain accounts, expose customers' personal data and shake trust in banks. Cyber security has become part of financial stability.
Prelims pointers
- Section 70B, IT Act: CERT-In may direct data centres, service providers and body corporates; defiance risks up to a year's jail, a fine up to Rs 1 crore, or both.
- CERT-In directions of 28 April 2022: listed cyber incidents must be reported within 6 hours of noticing them, and ICT system logs kept for 180 days within India.
- Section 70, IT Act: appropriate Government may declare a computer resource affecting Critical Information Infrastructure a protected system; unauthorised access draws up to ten years' jail and a fine.
- RTGS: minimum Rs 2 lakh with no upper ceiling; available 24x7x365 since 14 December 2020; settlement in the RBI's books makes payments final and irrevocable.
- NEFT: owned and operated by the RBI; available 24x7x365; the RBI imposes no amount limit, though a member bank may set its own.
- Master Direction, 2023: issued under section 35A of the Banking Regulation Act, 1949 and section 45L of the Reserve Bank of India Act, 1934, among other powers.
- IT Strategy Committee (2023 Master Direction, kept for commercial banks in 2026): at least three directors, chaired by an independent director with substantial IT expertise; meets at least quarterly.
- CSIRT-Fin works with the RBI, SEBI, IRDAI and PFRDA; CSIRT-Power has served since September 2024 as CERT-In's extended arm for the power sector.
Practise a UPSC-style question
With reference to the Indian Computer Emergency Response Team (CERT-In), consider the following statements:
1. It is the national agency for cyber incident response under section 70B of the Information Technology Act, 2000.
2. It functions under the administrative control of the Ministry of Home Affairs.
3. It may call for information from data centres and body corporates, and failure to comply is a punishable offence.
Which of the statements given above is/are correct?
- (a) 1 and 2 only
- (b) 2 and 3 only
- (c) 1 and 3 only
- (d) 1, 2 and 3
Show the answer
Answer: (c) 1 and 3 only
Answer: (c) 1 and 3 only. CERT-In belongs to the Ministry of Electronics and IT, so statement 2 falls.
Statement 1: correct. Section 70B of the IT Act, 2000 makes CERT-In the national agency for cyber incident response; the Centre appointed it by a notification of 27 October 2009.
Statement 2: incorrect. CERT-In works under the Ministry of Electronics and Information Technology (MeitY), not the Ministry of Home Affairs.
Statement 3: correct. Section 70B(6) lets CERT-In call for information and give directions to data centres and body corporates; section 70B(7) punishes failure with up to a year's jail, a fine up to Rs 1 crore (Rs 1 lakh until 2023), or both.
Eliminate: Judge statement 2 first: CERT-In sits in MeitY, so statement 2 is incorrect. Out: (a), (b), (d).
Trap: Swapped attribution. A cyber-security agency sounds as if it belongs to the Home Ministry, but CERT-In is MeitY's.
Remember: CERT-In: section 70B, IT Act, 2000, under MeitY; NCIIPC: section 70A.
More from the 26 October 2026 edition
- Operation Trident: NCB-led raids and PMLA action hit Myanmar-linked narco-hawala network National
- Oil spill off UAE shuts beaches: MARPOL, OPRC and IOPC Funds Environment
- UP orders re-check of electoral roll entries fed by computer assistants Polity
- Cyclone Arnab: Andhra Pradesh announces evacuations; NDRF, State forces deployed National
- Film certifier CBFC probes alleged leak from its e-Cinepramaan portal Polity
- Andhra Pradesh notifies polls in Kotia villages Odisha claims: inter-State boundary disputes Polity
- OBC creamy layer: Centre awaits SC directions to allocate 958 selectees Polity
- Section 163 BNSS curbs in Pasighat after Siang dam violence; RAF sent Polity
- IITM's new lab under Mission Mausam to trace Delhi-NCR pollution sources Environment
- Keralam ex-Governor reportedly recommended PSC chief's removal: how Article 317 works Polity